
Lakera Guard
For a straightforward look at an option like this, Lakera Guard is a sensible place to start. Visit lakera.ai to see live examples and up-to-date details. Lakera Guard brings a...
Sign in to rate this tool.
Overview
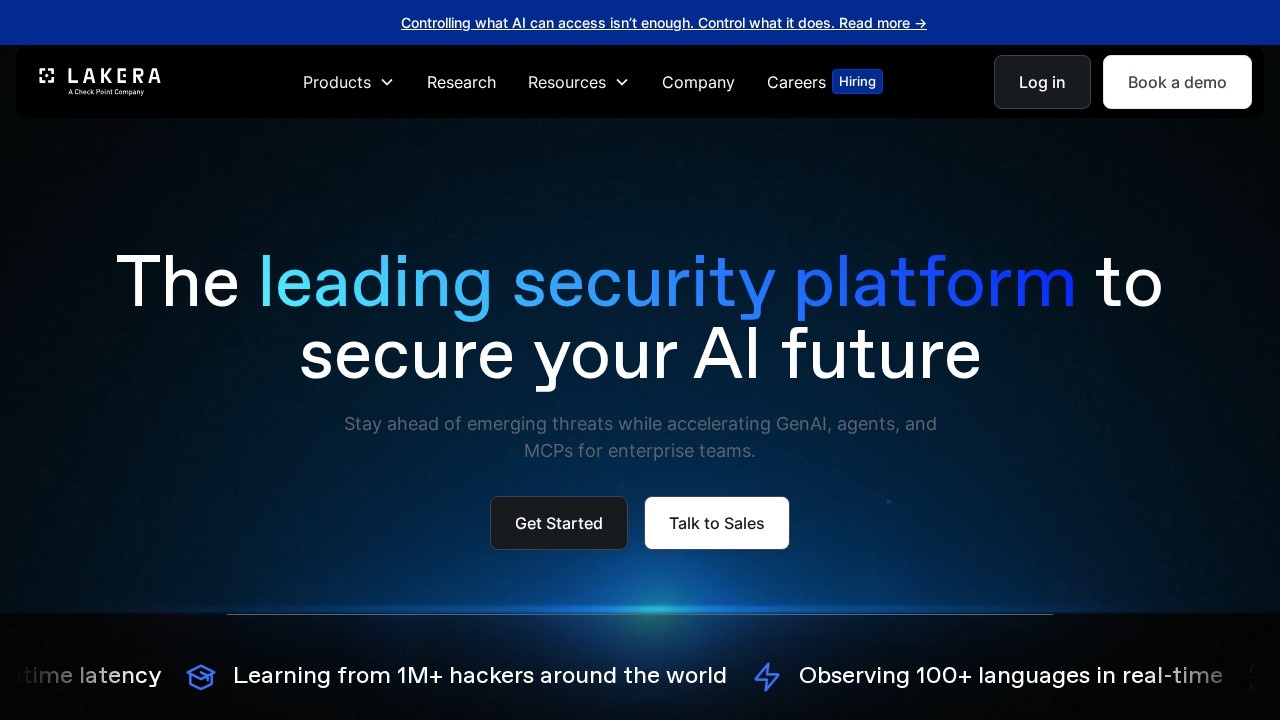
Lakera is a security platform for generative AI. Its product Lakera Guard protects AI applications and agents at runtime, and the wider platform covers how employees use AI tools and how companies test their AI systems. It is aimed at enterprise teams adopting GenAI, agents and MCP servers.
AI agent security
Runtime protection for AI applications includes real-time threat detection, prompt attack prevention and data leakage protection. The site says the system observes more than 100 languages in real time and delivers runtime latency under 50 milliseconds, so it can sit in front of a live application. Its threat knowledge is described as learning from more than one million hackers around the world, a reference to Lakera's public prompt-hacking challenges.
Workforce AI security
For employee use of AI, Lakera offers shadow AI discovery across apps and browsers, context-aware data protection in prompts and granular policy controls by user, app and action. This helps security teams see which AI tools staff use and stop sensitive data being pasted into them.
AI red teaming
Lakera also offers risk-based red teaming for GenAI, with vulnerability management, collaborative remediation guidance and simulations of direct and indirect attacks, so teams can find weaknesses before launch.
Getting started
You can get started from the site or talk to sales for enterprise deployment. The site highlights easy integration and says Lakera is used by companies from startups to the Fortune 500.
Who it suits
Lakera suits security teams and developers building customer-facing chatbots, retrieval systems or agents that can take actions, where a prompt injection could leak data or trigger harmful actions.
Things to consider
No filter catches every attack, so treat a guard layer as one part of defence in depth, alongside limiting what tools and data your agents can reach. Test the guard against your own use cases to check false positives, which can block legitimate users. Review where prompts are processed and stored, especially for regulated data. Red teaming is most useful when repeated after major model or prompt changes.
For teams just starting with AI security, the workforce discovery tools give a quick picture of current AI use across the company.
Details
- Pricing
- Freemium
- Release date
- 2026-01-07
- Last checked
- 4d ago
- Indexing
- index, follow
- Category
- Development
Suggest an edit
Sign in to suggest an edit.
Alternatives
 Orquesta AI PromptsOrquesta AI Prompts is a ai coding assistant that focuses on one thing: making the work easier. It skips unnecessary clutter and gets straight to useful output. For a straightforward...
 RaindropIt runs on a free model, so getting started is a low-risk decision. After a few sessions you will know quickly whether it fits. The flexibility shows when the same...
 AI Assisted Contember StudioThe tool may appeal to individuals and teams looking for help with ai coding work,...
 Maxim AIWhat stands out most is predictability. The same input produces dependable output, which matters when you are producing work for clients or publishing on a schedule. Away from the main...
 Featherless LlmBefore you decide, skip the speculation and look at the source. featherless.ai shows exactly what Featherless Llm does today and how to get started with it. Featherless Llm brings a...
 AdminforthPricing model listed: free. Pricing and...
 Modal ComRather than chasing every possible feature, Modal Com picks the ones that matter and does them well. That restraint is noticeable the first time you open it. Freelancers use it...
 OpensilverAccording to its listing, Opensilver is an AI tool...
 HeroHunt.aiHeroHunt.ai is an AI recruiter for sourcing and outreach. Tell it who you are looking for in plain language and it searches up to 1 billion public profiles, screens every…
 Iprep AIPricing is free, and there is no pressure to commit before you have seen results in your own context. Freelancers use it to keep client work moving, while in-house teams...
 TavilyThe feature set covers the basics well and adds thoughtful extras - keyboard shortcuts, reusable templates, and clean sharing options - without overwhelming you. Freelancers use it to keep client...
 MindstudioYou are not locked into a single way of doing things. Mindstudio supports your existing habits instead of forcing a new one, which makes adoption within a team much smoother....